Cyber Threats to Brazilian Educational Institutions: Key Incidents and Lessons Learned
| Shelf | AI & ML |
|---|---|
| Date in | |
| Readers | 872 |
Brazilian educational institutions face increasing cyber threats, particularly ransomware and insider attacks. Here’s a detailed analysis of incidents and strategies for improvement.
Introduction
Educational institutions are prime targets for cybercriminals, largely due to their handling of sensitive data and the interconnected nature of their networks. Public and private educational facilities must manage vast amounts of personally identifiable information (PII) including social security numbers (CPFs in Brazil), contact details, and student records. The lack of stringent security measures can make these institutions more susceptible to attacks, especially when various user groups—students, staff, and third-party contractors—interact with the network, each presenting different security demands.
In Brazil, this multifaceted environment creates unique vulnerabilities. Cybercriminals can exploit these weaknesses, leading to severe repercussions if a security breach occurs. Notably, attacks have been observed to result in the theft of sensitive PII, which can be used for phishing schemes, identity theft, or other malicious purposes. Through our Global Emergency Response Team (GERT), we've compiled a comprehensive analysis of cyber incidents targeting Brazilian educational institutions from January 2025 to June 2026. This report delves into common attack vectors, the nature of threats encountered, and offers insights into effective mitigation measures.
Key Findings and Statistics
Our analysis encompasses a variety of incidents within educational institutions across Brazil, with a concentration of attacks noted in São Paulo, a hub for economic activity. Further examinations revealed that the majority of incident responses originated from private institutions, accounting for roughly 60% of cases, with public institutions comprising the remaining 40%. The chart below illustrates the geographical breakdown of these incidents:
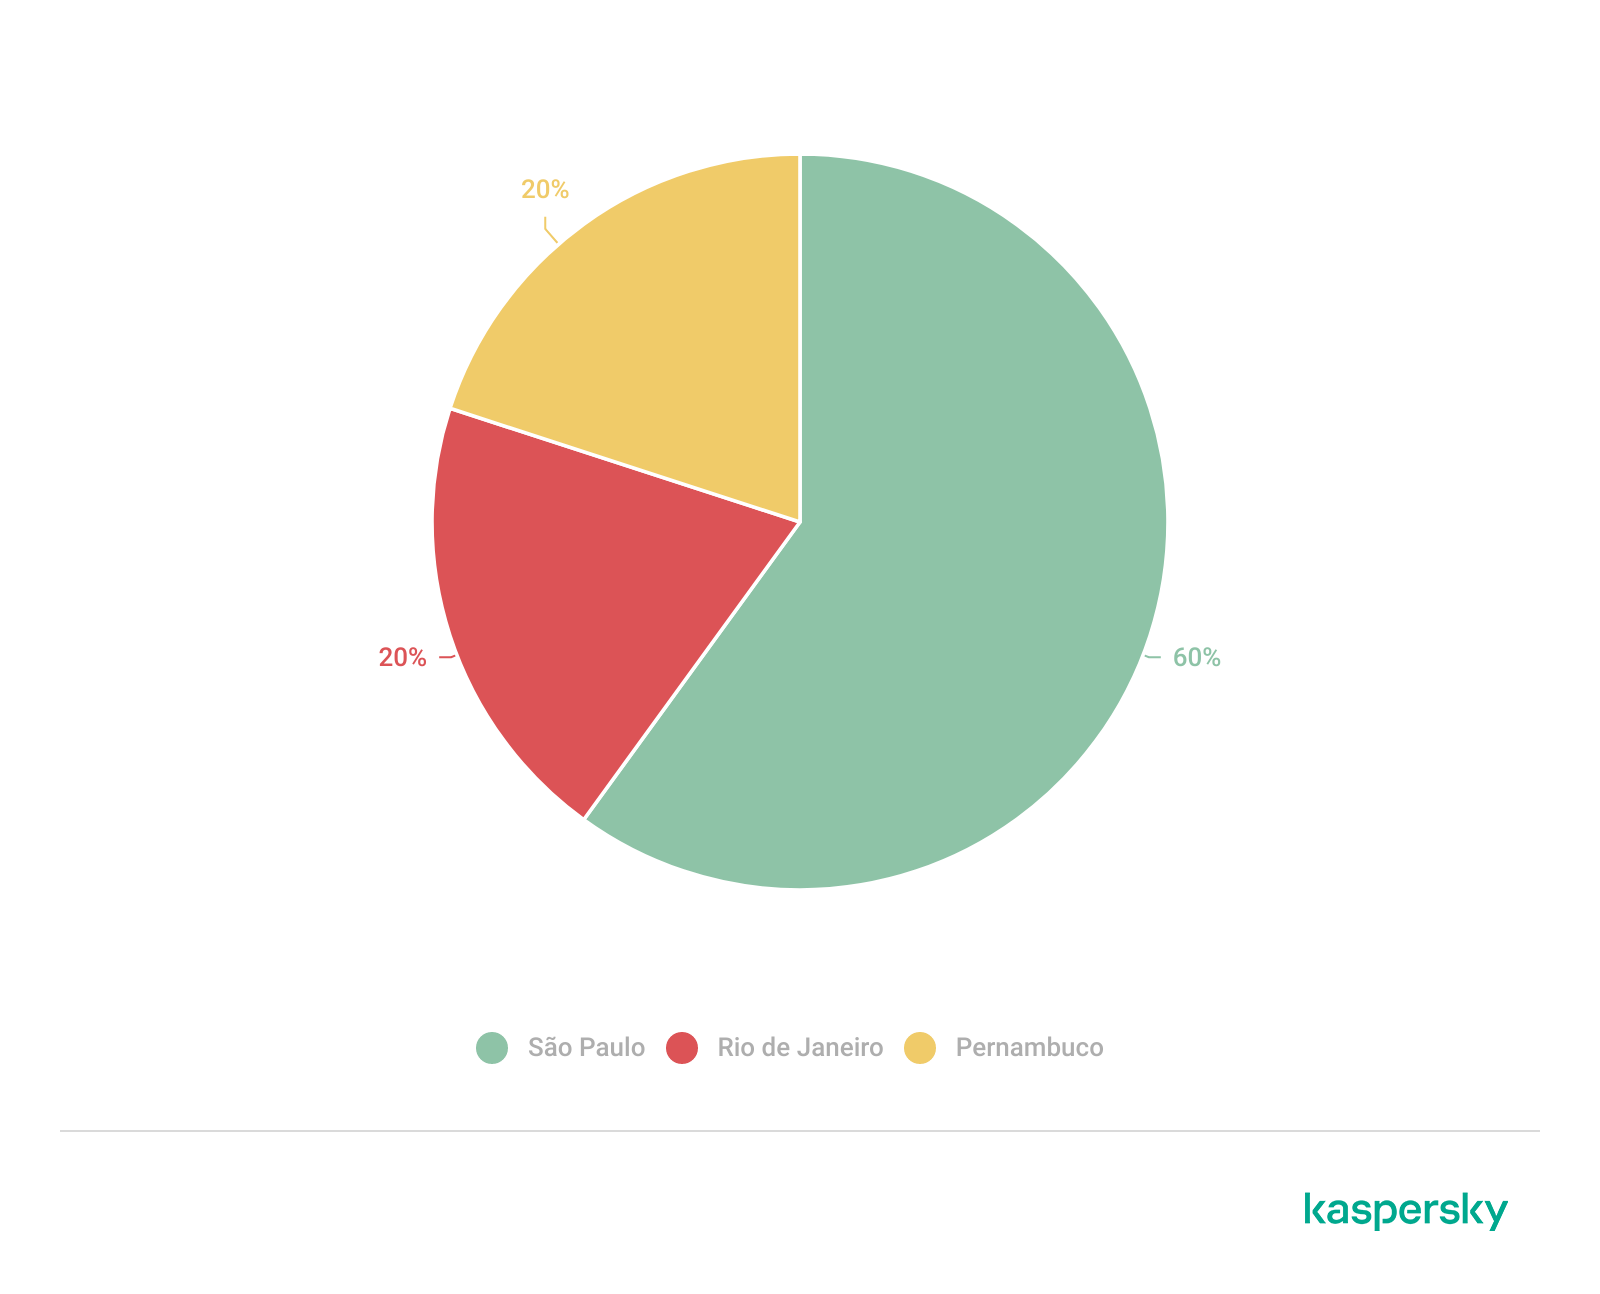
Geographical distribution of incident response requests at educational institutions
Our data indicates that the most frequent triggers for incident response requests were related to suspicious endpoint activities, followed by reports of encrypted files and the presence of unknown or suspicious files. The breakdown of reasons for incident response requests is further highlighted in the following chart:
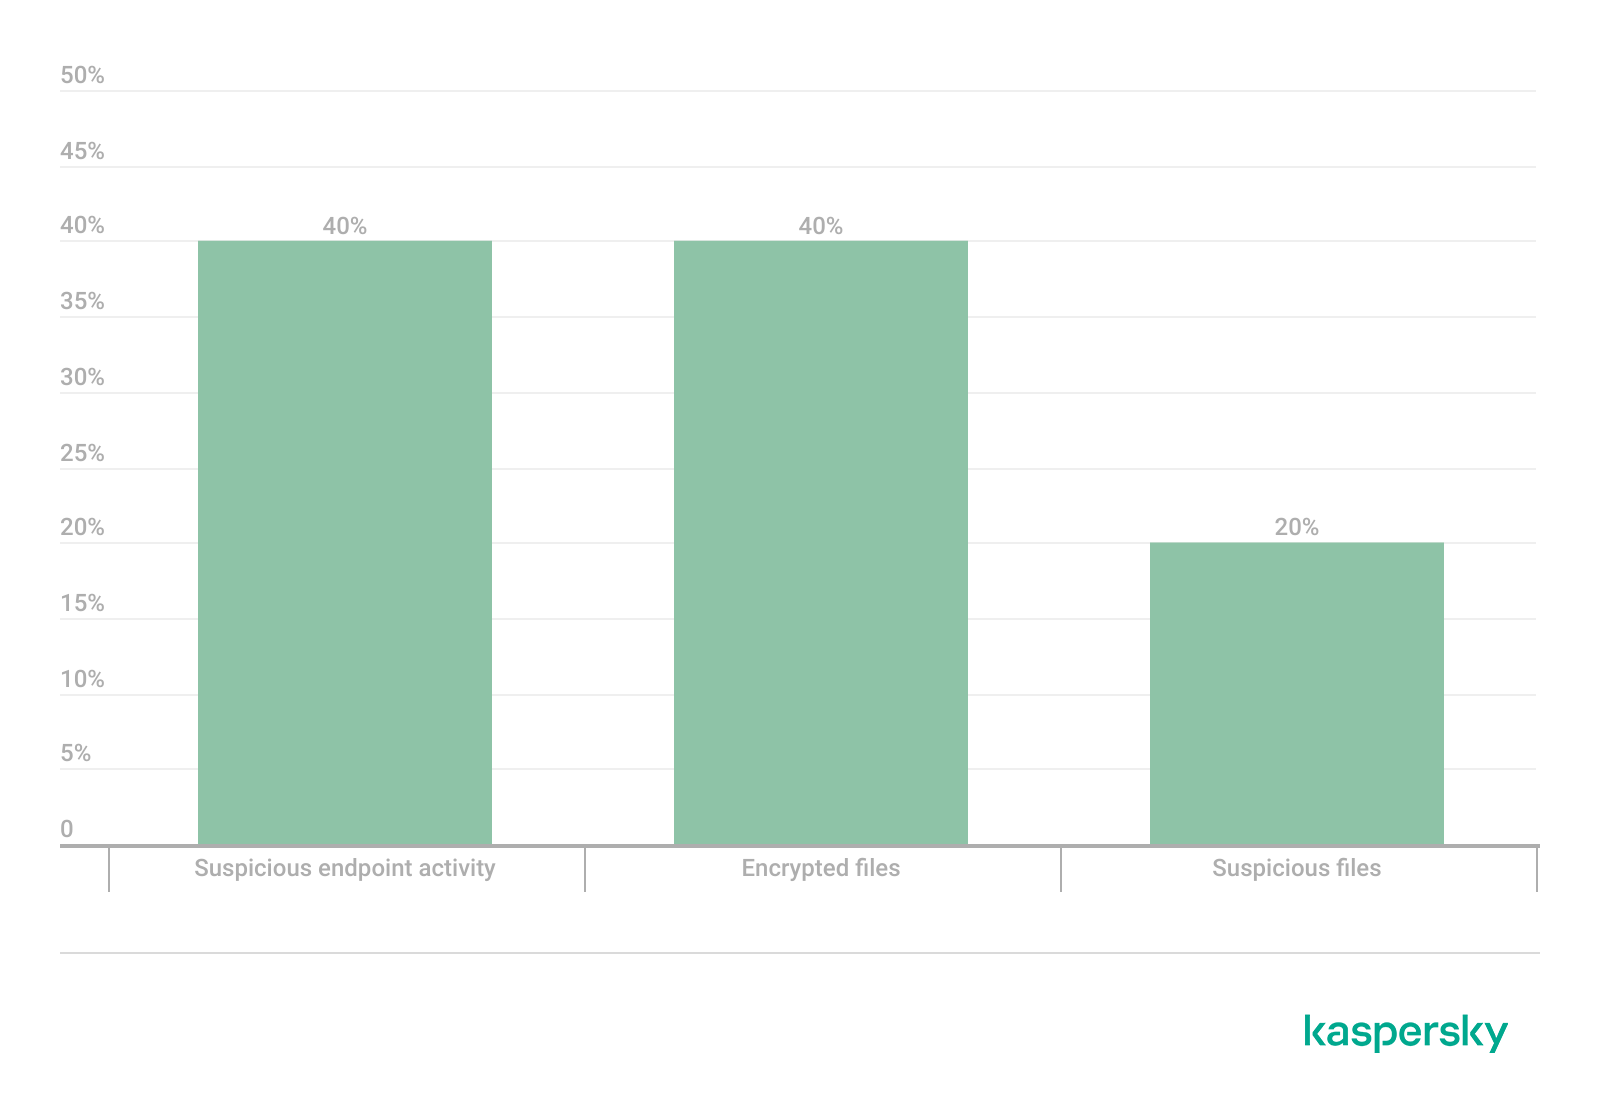
Incident response request reasons
High-severity incidents constituted approximately 40% of the cases we examined, with ransomware attacks being the primary issue. Notably, private institutions were predominantly targeted by ransomware attacks, whereas public institutions more commonly faced issues related to suspicious endpoint activity and privilege escalation attempts. Among the ransomware variants identified, DragonForce and LockBit 3 emerged frequently, with the latter's builder having been leaked in 2022, allowing attackers to utilize a privileged account to create effective malwares capable of bypassing security defenses.
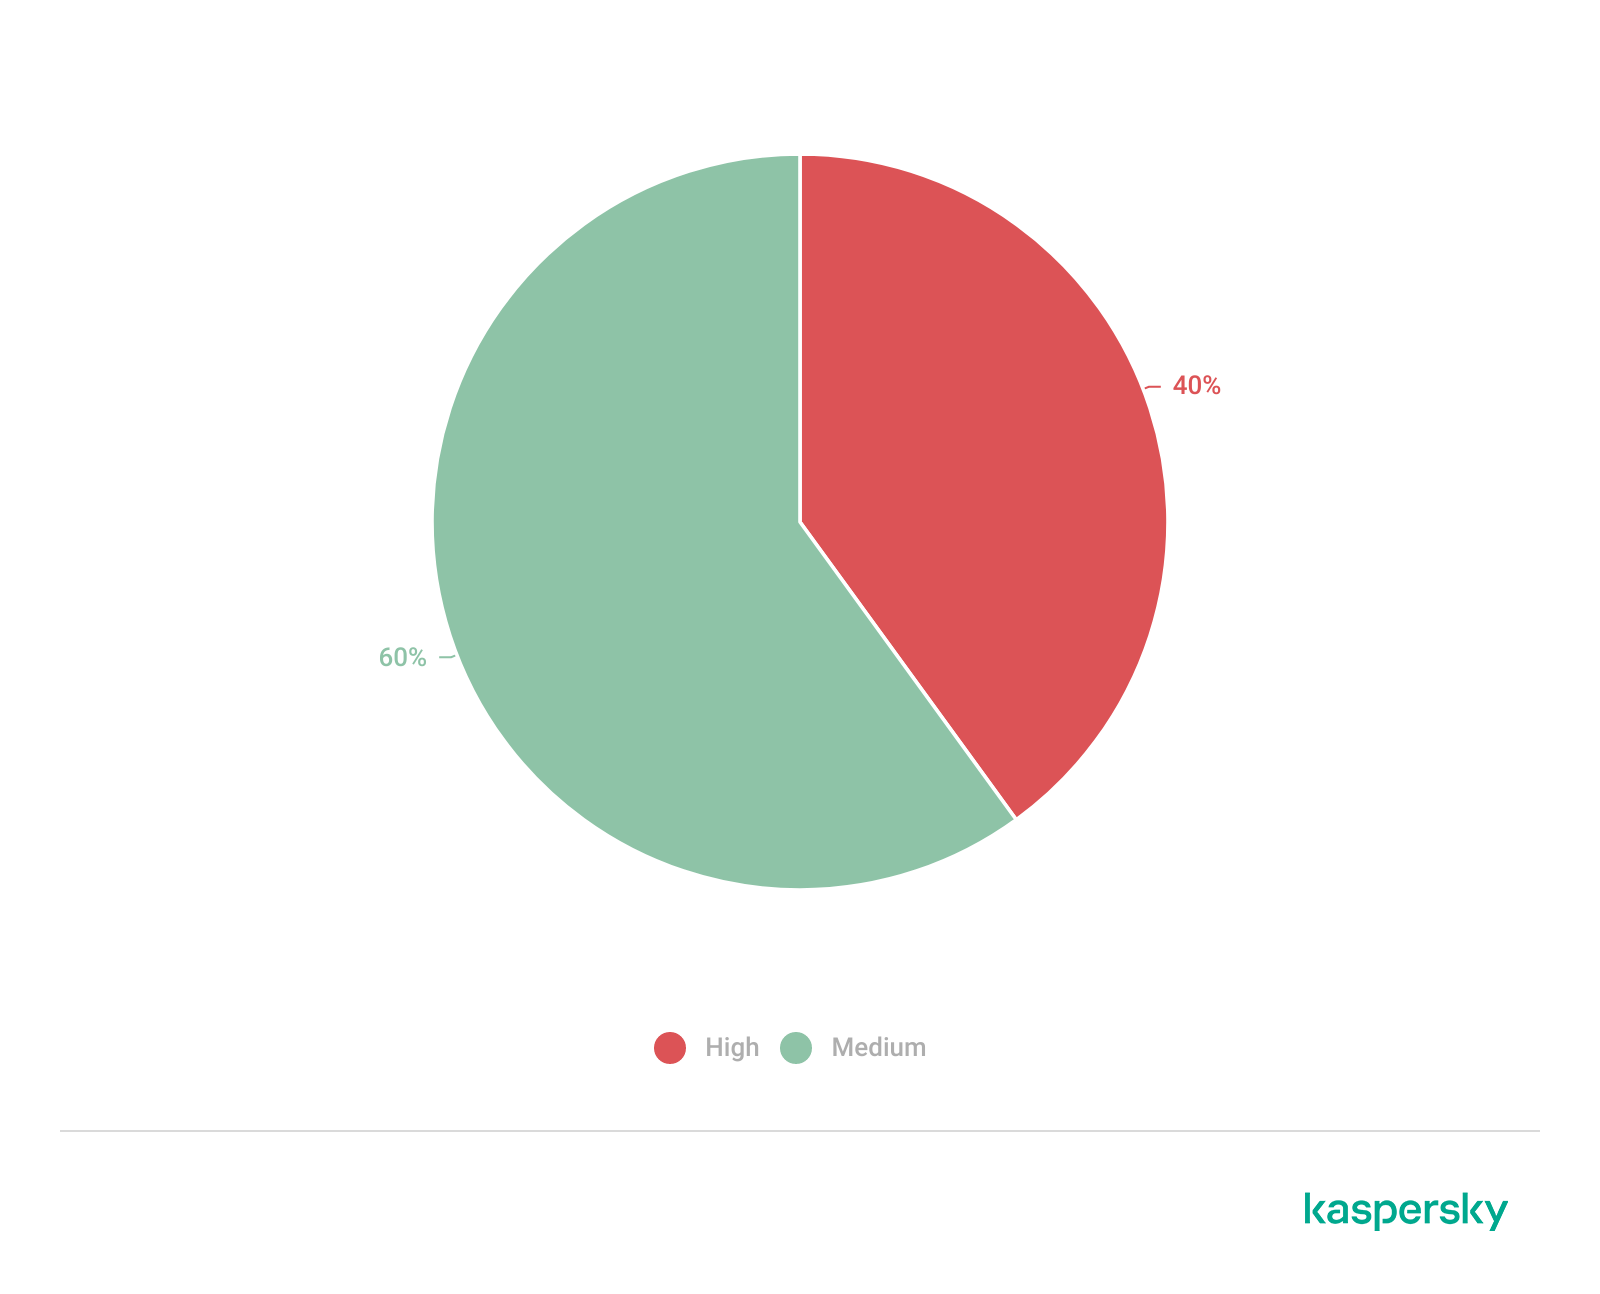
Distribution of incidents by severity
Common initial access points for breaches included the exploitation of valid accounts, vulnerable public-facing applications, and, to a lesser extent, insider threats. Susceptibility to insider threats was notably tied to weaknesses in user accountability and poorly monitored shared accounts.
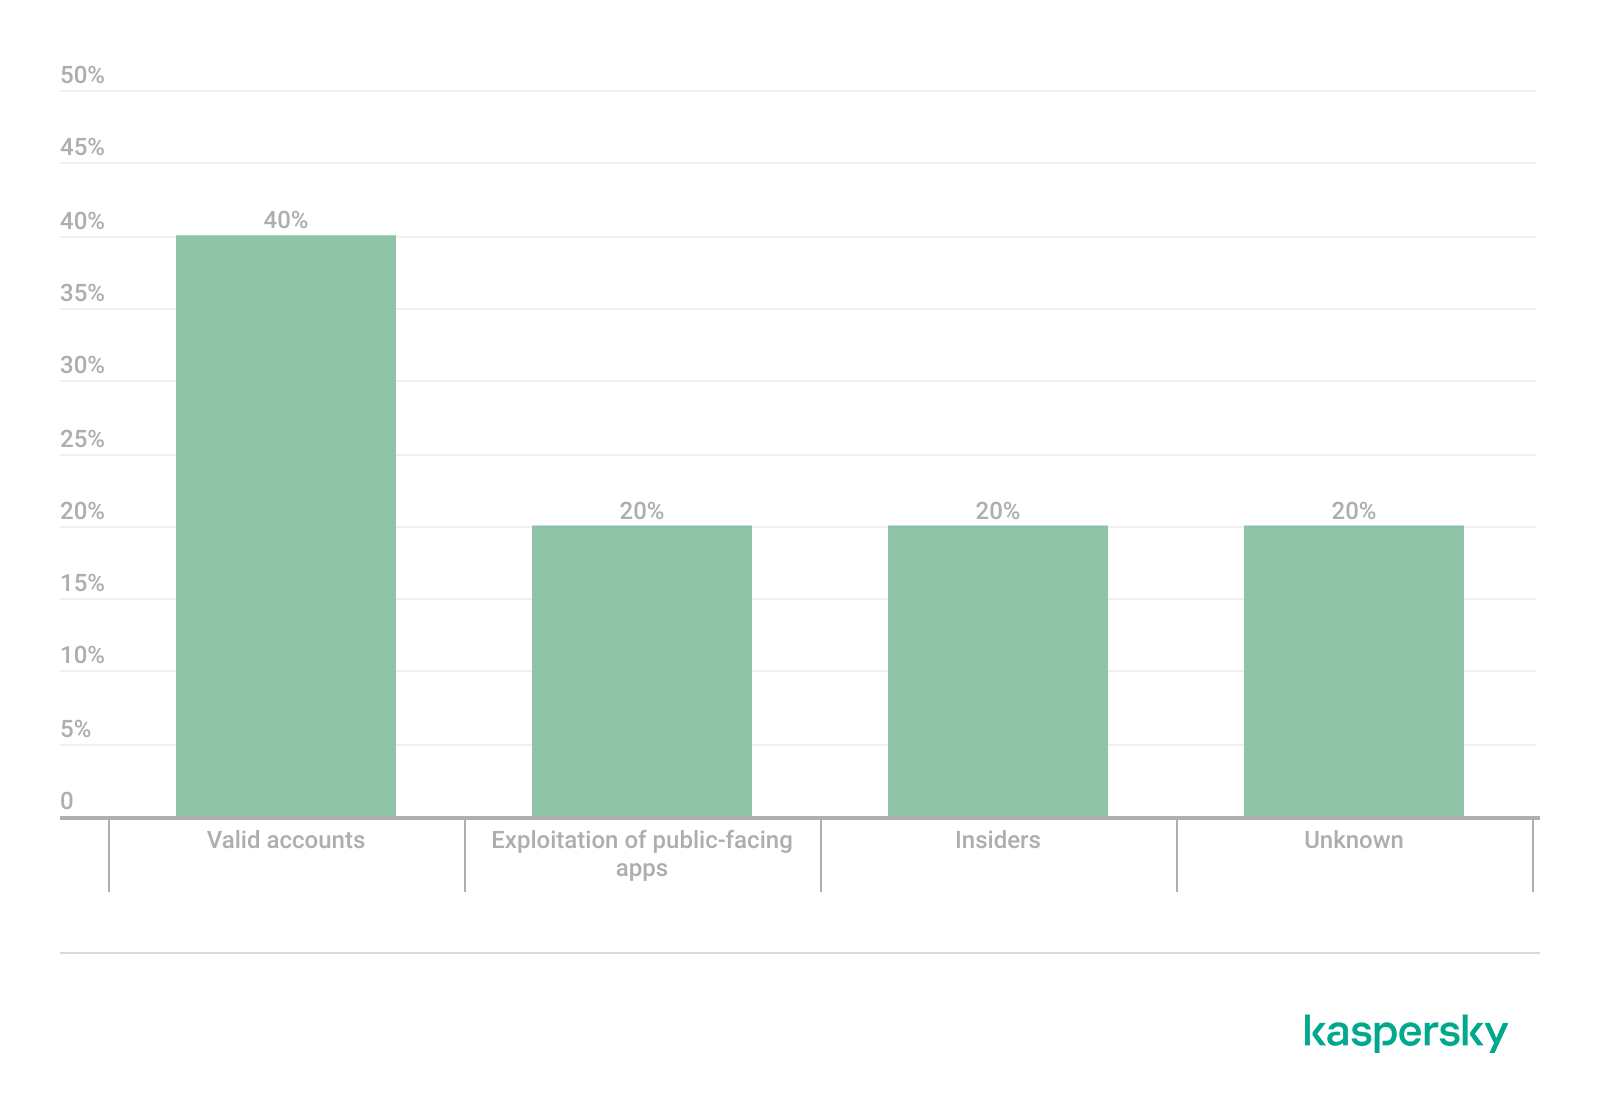
Initial access vectors
Interesting patterns emerged from our analysis: many incidents stemmed not from sophisticated attack strategies but from leveraging existing vulnerabilities, such as valid accounts, unsecured applications, and ineffective patch management. The predominance of ransomware incidents in private institutions highlights the financial motivations behind these attacks, as attackers often perceive that private educational institutions are more capable of meeting ransom demands than their public counterparts.
While many attacks were quickly identified and resolved within a few hours, the broader technical response took an average of 9.6 hours, indicating that the ramifications of a breach often extend beyond the immediate threat. Moreover, a troubling trend was observed with the continued use of unsupported systems, such as Windows 10, beyond Microsoft's end-of-support date, which exacerbates security risks as outdated OS versions are more easily compromised.
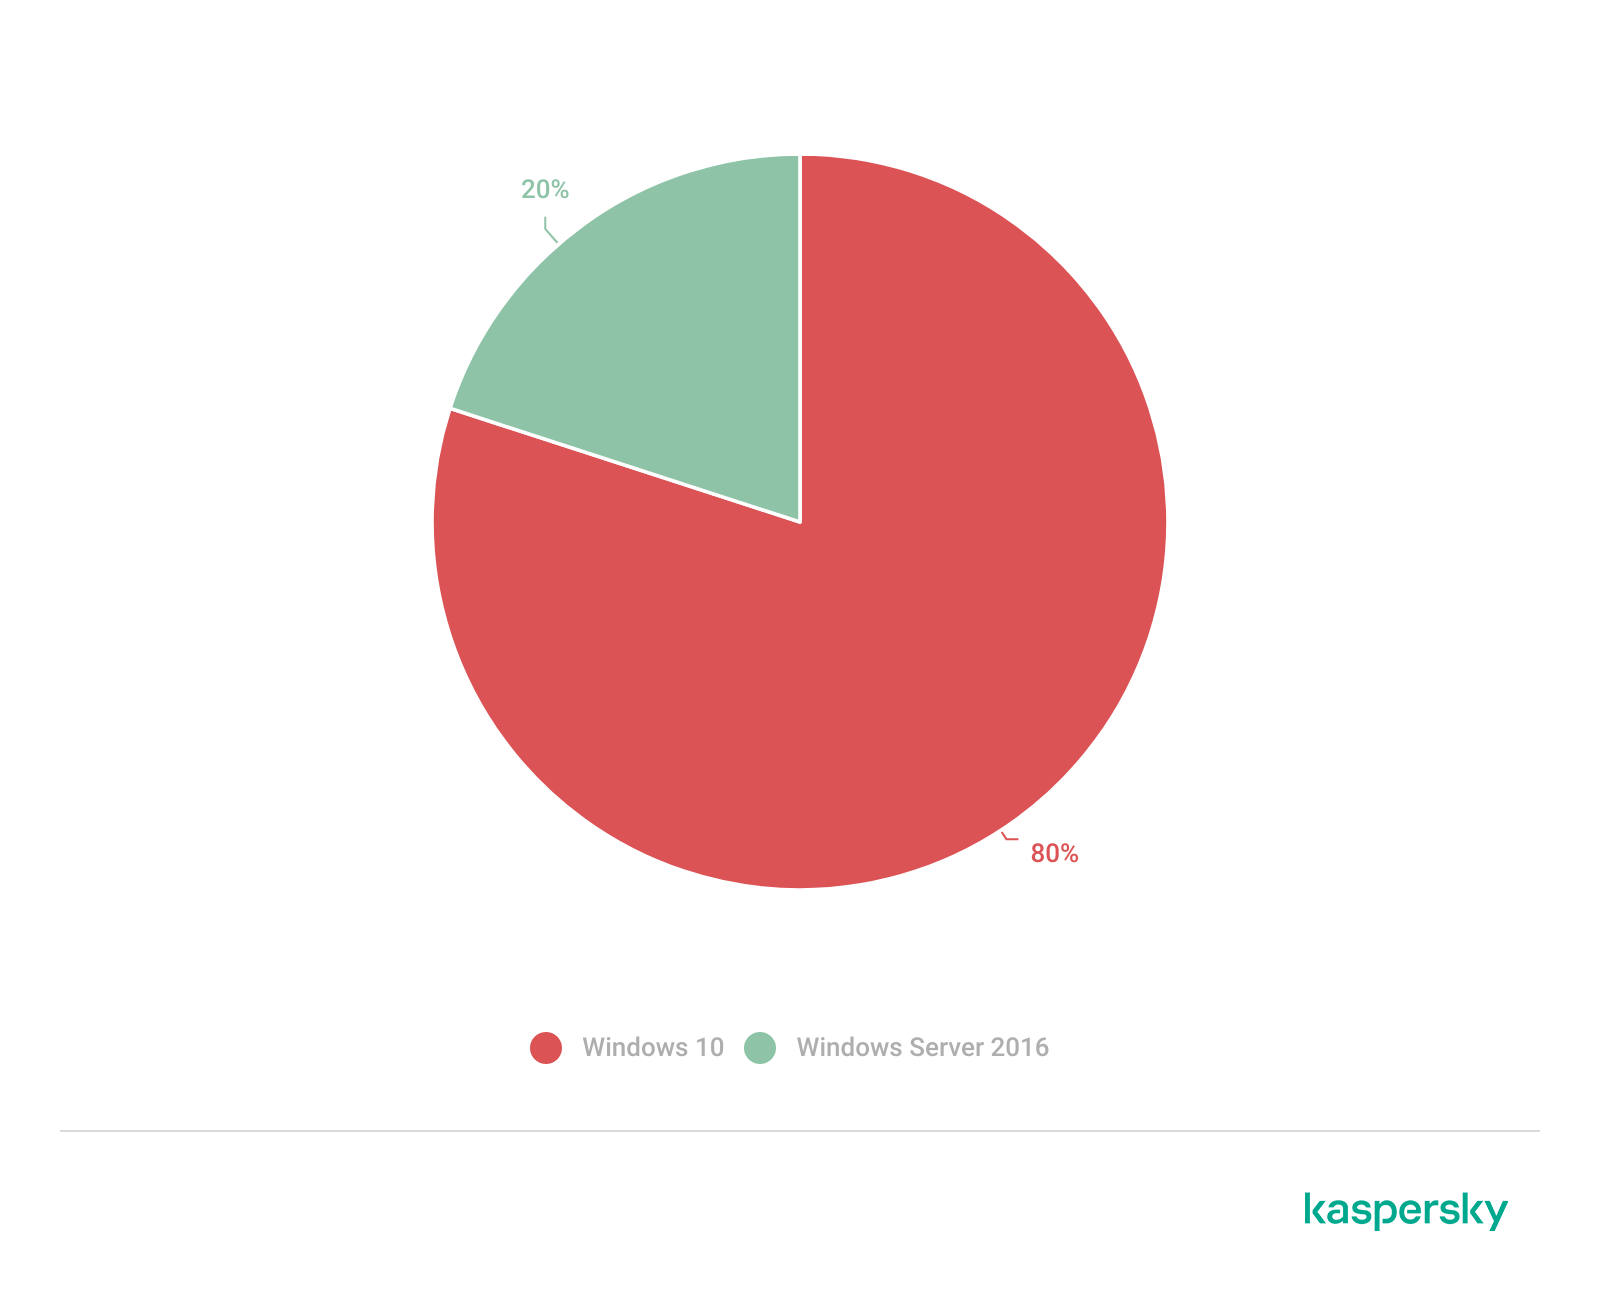
Obsolete systems in organizations
Case Studies of Noteworthy Incidents
Case 01 – Custom LockBit Builder Attack
In one notable incident, an educational institution was hit by a variant of LockBit ransomware generated using a leaked builder. The ransomware infiltrated the institution's systems via a valid account that had been compromised. Key internal resources such as file servers and databases containing sensitive student information were encrypted. Fortunately, there were no indications of data exfiltration.
An analysis of the ransomware revealed it was configured without options for impersonation or lateral spreading. Consequently, the attacker relied on manual tactics to disseminate the malware across the network. Forensic investigators tracked this lateral movement using PsExec, identifying compromised machines from the Update Sequence Number (USN) Journal that provided insight into the attacker’s path through the network.
The attacker deployed a script to disable system defenses, enabling remote access through RDP while simultaneously disabling key security features. The attempts were traced through registry modifications and service alterations. This incident highlights the critical need for secure credential management practices and robust defense mechanisms.
Case 02 – Remote Access via AnyDesk and DragonForce Ransomware
In another serious case, adversaries compromised a user account, utilizing it to install AnyDesk for remote access. Despite the attacker deleting logs after executing the ransomware, forensic investigation allowed the identification of the malicious sample through artifacts left behind. The analysis confirmed it was a variant of DragonForce, illustrating how remote access tools can facilitate successful ransomware attacks.
Case 03 – Insider Threat with Python Keylogger
This case underscores the risks associated with insider threats stemming from poor practices. In this scenario, users reported unusual file creations indicative of a keylogger. Investigation revealed suspicious executable files running from a commonly used user account, complicating the attribution process. The keylogger, developed in Python, recorded keystrokes and maintained hidden logs, necessitating a manual process for data collection to be executed by the insider. This case emphasizes the urgency of strict access controls and user accountability in shared environments.
Conclusions and Recommendations
The incidents analyzed reflect a spectrum of cyber threats faced by Brazilian educational institutions, primarily revolving around ransomware and insider threats. The data illustrates that exploitation of valid credentials and inadequate system management often facilitates these attacks. Accordingly, it’s imperative for educational institutions to implement robust cyber defenses, specifically by integrating multi-factor authentication (MFA) for all critical systems, particularly for remote access and email accounts.
Institutions should also conduct regular audits of administrative privileges, ensuring unnecessary accounts and permissions are eliminated to mitigate the risk of insider threats. Implementing structured access controls based on the principle of least privilege and avoiding the use of shared accounts are fundamental steps toward enhancing accountability.
Moreover, institutions should bolster their backup strategies, ensuring data is regularly backed up to isolated environments that are tested against potential threats. Monitoring and logging practices must be enhanced to support incident reconstruction, facilitating better forensic investigations post-incident.
Lastly, organizations must prioritize an effective patch management policy while fostering a culture of security awareness amongst users about the risks associated with compromised credentials and unauthorized software. By addressing these vulnerabilities and strengthening their cyber safeguards, educational institutions in Brazil can significantly reduce the risk of future incidents.
Observed Tactics, Techniques, and Procedures (TTPs)
A summary of observed TTPs in the incidents analyzed is outlined below, highlighting the common strategies employed by attackers to compromise educational institutions:
| Tactic | Technique | ID |
| Resource Development | Compromise Accounts | T1586 |
| Collection | Input Capture: Keylogging | T1056.001 |
| Execution | System Services: Service Execution | T1569.002 |
| Execution | Hijack Execution Flow: DLL | T1574.001 |
| Privilege Escalation | Exploitation for Privilege Escalation | T1068 |
| Lateral Movement | Remote Services: Remote Desktop Protocol | T1021.001 |
| Command and Control | Remote Access Tools | T1219 |
| Exfiltration | Exfiltration over Physical Medium: Exfiltration over USB | T1052.001 |
| Impact | Data Encrypted for Impact | T1486 |
Investing in the recommendations outlined will not only advance cyber resilience but also prevent the erosion of trust in educational institutions, which is paramount in their mission to educate and prepare future generations.


