Rethinking Trust in Container Images: Beyond Zero Vulnerabilities
| Shelf | AI & ML |
|---|---|
| Date in | |
| Readers | 748 |
Merely having zero known vulnerabilities in a container image doesn't guarantee its trustworthiness; understanding its origin and build process is crucial.
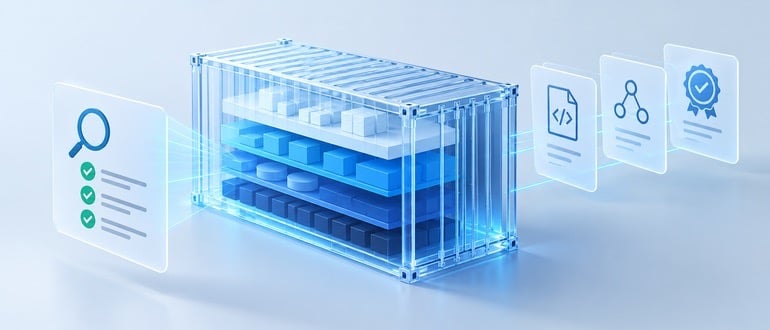
Container security often centers around the concept of vulnerabilities, most notably represented by the figure zero. When scanning a container image with tools like Trivy or Docker Scout and receiving a result indicating no known vulnerabilities, it's easy to fall into the trap of considering that image as safe for deployment. However, this interpretation glosses over critical aspects of trust and security.

Understanding the Limitations of Zero CVEs
Vulnerability scanners typically identify software components within an image and check their versions against vulnerability databases. When an image returns without any known CVEs (Common Vulnerabilities and Exposures), the real takeaway is limited to the absence of known vulnerabilities in the identifiable components. Continuously, new vulnerabilities are disclosed, meaning an image with a clean scan today could be flagged tomorrow. The dynamic nature of vulnerabilities underscores that a scanner’s results can shift based solely on new information, regardless of whether the image itself has changed.
The challenge amplifies when you consider the accuracy required from these scanners. If the software within an image isn't recognized—due to incomplete metadata or binaries added outside standard package management processes—detection becomes unreliable. Even more concerning is that malicious software can exist without a CVE, meaning a zero CVE status doesn't equate to a lack of malicious intent.
Trusting the Source
A clean vulnerability assessment leads to an immediate follow-up question: Who built this image, and under what circumstances? Using public registries might simplify the consumption of images, but they do not inherently clarify their origins. The familiarity of an image name does not necessarily correlate with understanding its development history, source code utilization, and dependency management.
To ensure trust, several factors should come into play:
- Image Digest: This digital fingerprint specifies the exact artifact being pulled.
- Cryptographic Signing: Ensures that a particular trusted entity signed the artifact, adding an additional layer of confidence.
- Provenance: Evidence detailing the source, build process, and identity of the creator enhances trust.
It's essential to recognize these elements as complementary controls. While a signature confirms that a trusted identity built the image, it does not guarantee that the image aligns with expected source code or dependencies.
The Contents Matter
A common misconception is that the presence of unnecessary software components within an image is benign. For example, many container images might retain shell environments, compilers, or package managers, which can still pose vulnerabilities. An attacker's success often hinges on the tools and utilities available within a compromised container.
Thus, best practices should not only focus on vulnerability elimination but ensure that the resulting artifact is streamlined—composed solely of intentional, identifiable components tied back to a rigorous build process.
Ongoing Trust Post-Deployment
The lifecycle of trust doesn't halt at deployment. A new vulnerability could emerge at any moment, and dependencies may reach end-of-life status without warning. As a result, continuous evaluation of artifact trust is mandatory. It's here that we must differentiate between the artifact’s immutability and its security status, which can fluctuate based on newly available information or advisories. A static image can suddenly reveal new risks as circumstances evolve.
Improving the Default for Developers
It's unreasonable to expect every developer to act as a meticulous investigator for each container they pull. Just as unrealistic is the notion that security teams can manually vet every image that enters an enterprise setting. There needs to be a paradigm shift, providing developers with access to images that inherently come with substantive evidence about their provenance and build processes, minimizing the demand for extensive manual checks.
While vulnerability scanning remains a cornerstone of the security process, its insights should not be the sole bedrock of trust. A mere count of known CVEs can help inform exposure levels and remediation priorities, but it shouldn't overshadow the necessity for other forms of evidence concerning an image's origin, contents, and creation methodology.
In summary, a container image can boast zero vulnerabilities on paper yet still pose significant trust risks. Engineers and product managers must dig deeper than surface-level scans, performing due diligence to understand the source and lifecycle of an image thoroughly. As we integrate more advanced security practices, the priority should shift to developing clearer standards for image provenance and safer development workflows.